The Ledger Wallet Hack is Not Just a Crypto Problem
Our top stories this week:
- Ledger confirms spy chip implant behind wallet crypto thefts
- Fridge hack costing millions and sparking fires stemmed from poor security
- PSA: Google is silently linking your phone number across all signed-in accounts
- ‘Nightmare Scenario’: Zero-Click Spyware Is Infecting Phones via Targeted Ads
TWIP Live 🔴
Updates from the Team
News Briefs
This week's news briefs discuss Android's next gen secure enclaves for AI security, the Pwn2Own conference in Ireland, and more!
 Jonah Aragon
Sources
Ledger confirms spy chip implant behind wallet crypto thefts
Several ledger hardware crypto wallets resold in Southeast Asia by CryptoBilis have been found to contain a modification that read the screen and sent the seed phrases back to an unknown party via an embedded SIM card. Investigation is still ongoing on who's behind the attacks and how widespread the compromise is.
 Bill Toulas
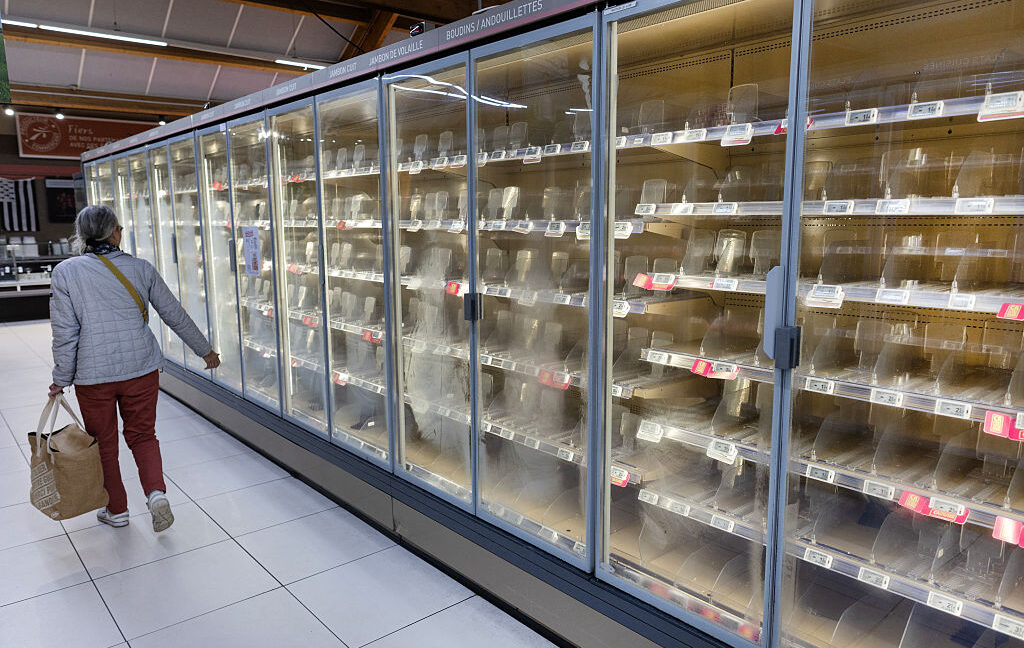
Fridge hack costing millions and sparking fires stemmed from poor security
Earlier this week, a hack impacted supermarkets across Europe but mostly in France. Attackers raised the temperatures in grocery store fridges and freezers to spoil food and in some cases start fires. It turns out that many of the hacked devices were running outdated firmware and using poor default passwords that were easily findable online.
 Dan Goodin
PSA: Google is silently linking your phone number across all signed-in accounts
Google has quietly updated their policies to now add your SIM number to every Google account you're signed into on your Android phone. The original intent of this feature (according to Google) was to ensure that you don't forget to keep your information up-to-date, but it's pretty easy to see how this could be unwelcome behavior if you're signed into secondary accounts, work accounts, or more.
https://www.androidauthority.com/google-auto-phone-number-verification-android-3723117/
‘Nightmare Scenario’: Zero-Click Spyware Is Infecting Phones via Targeted Ads
For the first time ever, researchers have confirmed state-level spyware is being spread through advertising. This is made possible in part because the advertising delivery system - called Real-Time Bidding - is already a privacy nightmare, making ads a perfect attack vector to deliver a payload only when it detects a specific device or device meeting specific criteria. This the first time a zero-click mercenary malware has been confirmed using this attack vector.
 Matt Burgess and Lily Hay Newman
Forum Updates
 jonah
 Mxyzptlk