X's Encrypted Messenger, X Chat, Disappears From the App Store and the Google Play Store

X Chat, X's dedicated end-to-end encrypted messaging app, has disappeared from both Apple's App Store and the Google Play Store.
According to 9to5Mac, the app's disappearance is not due to the stores removing the app but instead X removing it of its own accord.
X Chat was essentially a standalone version of direct messages on X itself. It only released a few months ago in April of this year, making it a very short-lived app if they have officially discontinued it. The official XChat account didn't mention anything about it either.
The bizarre thing is that X didn't seem to announce that it would be discontinuing the app to give people time to migrate away or let them know they should uninstall the app while it stops receiving updates.
X's documentation still mentions the X Chat app, so it seems they haven't even bothered to update their official support pages to reflect the change. As a side note, they can't seem to decide officially if it's called X Chat or XChat.
When you try to DM someone on X, it calls that "X Chat" and explains that it's E2EE.
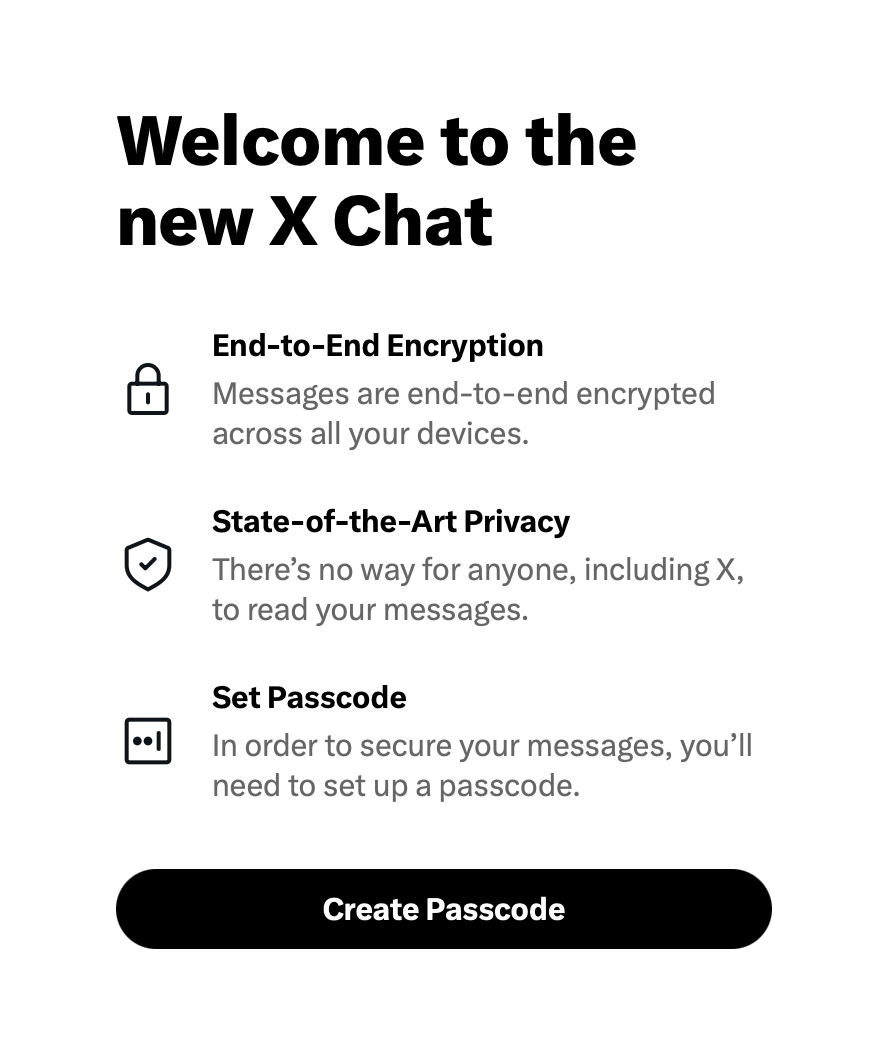
You don't need the X app either, E2EE messaging seems to be the default for direct messages on the website as well.
Hopefully, the removal of the XChat apps doesn't signal a move away from encrypted messaging on X, it's genuinely good that they offer this as a feature.
Other platforms have taken a stance against E2EE messaging. Instagram removed E2EE support for its messages. TikTok stated that they wouldn't add E2EE for "user safety" reasons.
That being said, X's approach to E2EE leaves a lot to be desired. According to their documentation, when you start an encrypted conversation, the private key is actually sent to X's infrastructure and is only protected by a flimsy 4-digit PIN.
Not only is a 4-digit PIN easy to guess, it's so quick to brute force that it's effectively instantaneous using any modern computer. Supposedly, the open-source Juicebox protocol X uses prevents brute forcing and hardware security modules are used to rate limit guesses.
They also state that their encryption lacks forward secrecy, so an attacker who is able to gain access to the private key of one of your registered devices will have access to all of your messages. Supposedly, plans are in place to introduce forward secrecy in the future.
Community Discussion